Attackers exploited a previously unknown flaw in Citrix NetScaler gateways for at least three weeks before anyone confirmed it. Mandiant told CyberScoop that the earliest known exploitation of the vulnerability, which carries the Common Vulnerabilities and Exposures identifier CVE-2026-88772, occurred on September 3. A second zero-day, CVE-2026-88771, was being exploited as well, and Citrix confirmed both in its September 27 bulletin. Mandiant’s chief technology officer said dozens of organizations were affected and attributed the activity to advanced and suspected state-sponsored actors. While the technical analysis published by Mandiant and the Google Threat Intelligence Group did not name an actor, it noted that North American and European organizations in the government, financial services, technology, education, and legal sectors were likely impacted.
NetScaler appliances sit at the network edge, and edge devices make a preferred door for reasons that have little to do with any single product. Google’s analysts pointed out that these appliances face the internet, sit outside the reach of endpoint detection and response tools, and also tend to hold credentials that carry an intruder deeper into a network. Vulnerabilities in such devices accounted for 48% of enterprise-related zero-days last year, according to Google figures CyberScoop reported. In the case of these NetScaler incidents, once inside, the actor installed web shells and a tunneling tool that pushed traffic from the appliance into the victim’s network. In at least one intrusion, that tunnel supported manual reconnaissance and credential theft.
Remediation Guidance Matters
Mandiant instructed organizations to assume that credentials stored on a compromised appliance may have been exposed, and to rotate them after the appliance is patched. The rotation list included appliance administrator accounts, directory bind accounts used for Lightweight Directory Access Protocol, shared secrets for Remote Authentication Dial-In User Service, application programming interface credentials, and the certificates and private keys held on the device itself. Read as a whole, the list described the machinery by which an organization decides who is who. Defenders are, in effect, being told to treat the identity material around the gateway as suspect. The question that follows a gateway compromise is not only what was taken, but whom the network still trusts…and why.
In this instance, Citrix stated that an update would not remove potential compromise artifacts, which is why they recommended deploying a new, updated instance when a compromise is suspected. The Cybersecurity and Infrastructure Security Agency (CISA) encourages organizations to check for signs of compromise before patching, and to preserve forensic evidence when a compromise is suspected, because updates may reduce forensic visibility. Similarly, the United Kingdom’s National Cyber Security Centre (NCSC) recommends isolating affected systems where possible and replacing them with new, fully updated ones, while noting that doing so may cause a service outage.
No Easy Remedy
CISA acknowledges that updating these appliances can be complex and may require downtime. Mandiant noted that broad internet isolation can cause significant disruption for organizations with remote workforces and recommends a phased approach that prioritizes patching while compensating controls are applied. Unfortunately, all of those decisions are made while the facts are still incomplete. Citrix itself cautions that its generic indicators of compromise might fail to identify actual compromises and advises customers to retain experienced forensic investigators. Defenders therefore face an investigation rather than a patch cycle, and an investigation depends on a group of people – including outside specialists – talking to one another over an extended period.
Citrix recommends forwarding appliance logs to an external logging or security information and event management (SIEM) platform. Mandiant adds that several of its recommended detections depend on telemetry NetScaler does not forward by default, which is a reminder that a compromised device is a poor witness against itself.
Communications May Also Be Compromised
If the response channel authenticates through the same directory the gateway was trusted to query, the team coordinates inside the same environment it is trying to measure, and a channel that depends on suspect identity material inherits the suspicion. While the sources reviewed for this piece do not describe any incident response channel being read in this campaign, that behavior has been documented elsewhere. Microsoft’s research on an extortion group they tracked as DEV-0537 described the actor joining targets’ crisis-communication calls and internal discussion boards, including incident response bridges. Microsoft advised organizations to develop an out-of-band plan for responders that will remain usable for multiple days while an investigation occurs. The group and the period may differ from the NetScaler campaign, but the exposure of a response team’s channels does not.
Kudos to the Responders
The public response to this campaign merits recognition, starting with CISA adding both exploited vulnerabilities to its Known Exploited Vulnerabilities catalog on Sunday, September 27, citing reports and partner threat intelligence that confirmed exploitation worldwide. Federal civilian agencies were directed to secure any vulnerable appliances by September 30, and the NCSC followed with its own alert the next day. Once the flaws were confirmed, the defensive community moved quickly. The earliest warnings, however, traveled privately as agencies and suppliers contacted organizations directly before the vendor’s public confirmation. The advisories carry the technical response, while the channel a team trusts with its own deliberations has to be chosen long before the next zero-day arrives.
Where Mattermost Can Help
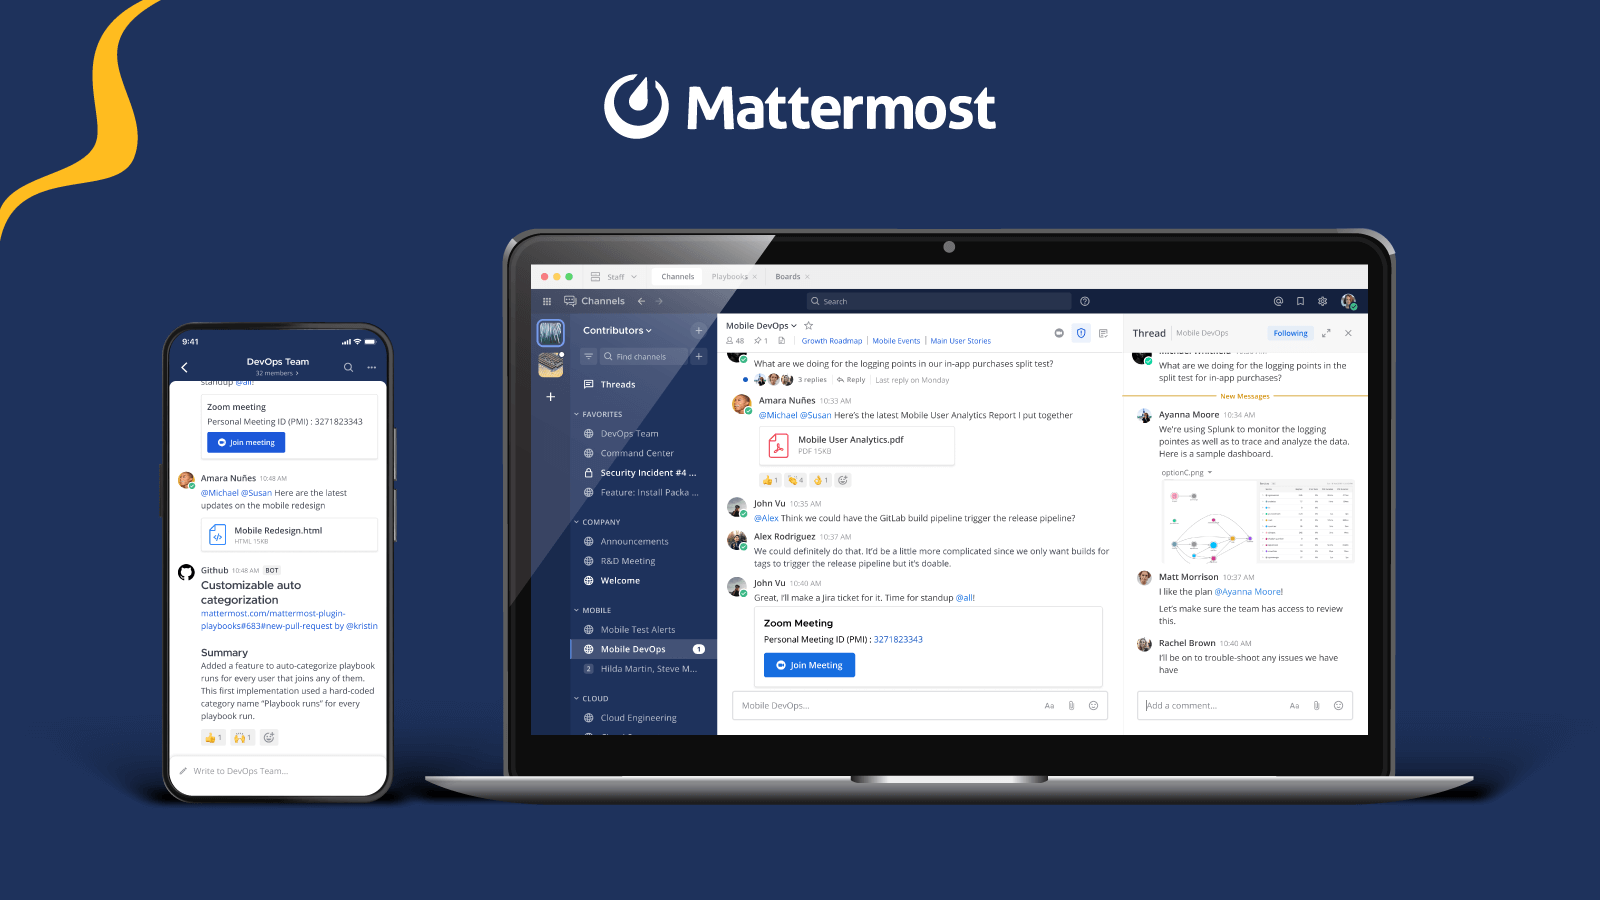
Mattermost’s out-of-band deployment guidance takes up the identity problem directly, with a design that calls for a dedicated identity provider independent of the organization’s primary single sign-on or identity provider. Authentication is isolated from primary infrastructure, and user accounts are loaded before an incident begins.
Independence carries obligations. The same guidance instructs operators to treat the out-of-band environment as Tier 0 and to run failover exercises every quarter. It also specifies multifactor authentication, secure vaults, and emergency tokens, and it directs operators to rotate secrets regularly. A separate identity provider is one more system to harden and monitor. Rehearsal is part of the design, not an afterthought, because an out-of-band channel that nobody has tested is likely to fail when it is needed.