Trusted Devices, Workflows and Decisions
Operational resilience depends on trust, but not in just one place.
Organisations need confidence that the right people and devices are connecting to critical systems, that information is moving securely, that workflows are governed, and that decision-makers are working from reliable information. In increasingly distributed environments, those layers of trust are interconnected. If one breaks down, the effects can quickly spread into the wider operation.
For organisations working across hybrid infrastructure, sensitive environments, partners, third parties and geographically dispersed teams, the challenge is no longer simply whether a communications channel is secure. The more important question is whether the organisation can trust the device, the connection, the workflow and the decision that follows.
Five questions leaders should be asking
For CISOs and operational leaders, the challenge is not simply whether individual security controls are working. It is whether trust can be maintained across the entire operational environment as conditions change.
Five questions help expose where assumptions may still exist:
- Can we continuously verify the devices connecting to sensitive operational environments, and remove access when a device becomes compromised or untrusted?
- Can authorised devices establish secure connections that remain resilient against current and emerging cryptographic threats?
- Do teams coordinate through workflows that are governed, auditable and under our control?
- Can that environment remain independent and available if primary communications, identity or cloud services are compromised or isolated?
- Can decision-makers continue to trust the information, context and records produced throughout an incident?
These are not questions that should be answered for the first time during a breach. They need to be addressed in the architecture, systems and workflows organisations rely on every day.
Modern operations create more points where trust must be established
Critical operations rarely take place inside a single, tightly controlled environment.
Teams may be distributed across several locations. Infrastructure may span on-premises systems, private cloud environments and remote or isolated networks. Partners may need access to shared workflows, while users operate across different security domains and device types.
Each connection introduces another point where trust must be established and maintained. For organisations responsible for critical services, that challenge increasingly sits alongside formal expectations around cybersecurity governance and resilience.
In Singapore, the Cyber Security Agency regulates owners of Critical Information Infrastructure under the Cybersecurity Act and associated Codes of Practice. The updated 2026 Cybersecurity Code of Practice for CII reflects the increasing attention being placed on the resilience of systems supporting nationally important services.
For government, financial services and critical infrastructure leaders, trust therefore needs to satisfy both an operational requirement and a governance one. Organisations need to know not only that systems are secure, but that access, connectivity and operational workflows remain appropriately controlled as environments become more distributed.
Most organisations already use multiple layers of security to manage this complexity. Identity systems authenticate users. Encryption protects information in transit. Collaboration platforms support communication, and workflow systems help teams coordinate activity.
The challenge is that operational resilience depends on those layers working together, not simply existing independently.
A secure message originating from an untrusted device can still create risk. A trusted device entering an ungoverned workflow can create a different problem. Even well-protected information has limited operational value if the people receiving it cannot establish context, provenance or authority.
Trust needs to persist across the whole environment.
Trust starts before information enters the workflow
The first step is establishing confidence in the devices and connections participating in that environment.
For organisations working across government, defence and Critical Information Infrastructure, this goes beyond checking a username and password or authenticating a device once at the point of connection. Trust needs to be continuously maintained as operating conditions, device status and risk change.
Devices need to establish authenticated, cryptographically secure connections before they begin to exchange sensitive information. Organisations also need the ability to continually reassess that trust and revoke or remove access if a device becomes compromised, behaves unexpectedly or no longer meets policy requirements.
That makes device trust a continuous operational process rather than a one-time security check.
It also means considering whether today’s cryptographic architecture is prepared for tomorrow’s threats.
Post-quantum cryptography readiness is increasingly becoming part of long-term cyber resilience planning, particularly where sensitive information needs to remain protected for many years. Arqit approaches this challenge through quantum-safe symmetric key agreement, helping authorised endpoint devices establish secure cryptographic relationships while supporting greater control over which devices are permitted to participate in sensitive operational environments.
This shifts cryptographic resilience from a future technology discussion into a present-day operational requirement. Organisations need mechanisms that can establish trusted connections across distributed devices, maintain that trust as conditions change and withdraw it when confidence in a device is lost.
The stronger the foundation of device and connection trust, the stronger the environment in which operational work can take place.
“Operational trust has to begin before information enters the workflow. Organisations need confidence that the devices connecting to critical environments are authorised, continuously trusted and able to establish secure connections without adding unnecessary complexity or exposure.”
Seán Carnew, Senior Director: Government & Defence, Arqit
Trust has to continue through the workflow
Secure connectivity is only the beginning.
Once information enters the operational environment, teams still need to know where it should go, who should receive it and what should happen next. For cyber, operational and mission teams, those workflows may include threat intelligence sharing, incident escalation, task coordination, approval chains, automated alerts or executive reporting.
The effectiveness of those processes depends on clear access controls, known participants, governed information flows and persistent records of activity. Without that structure, secure communications can still result in fragmented decisions and inconsistent action.
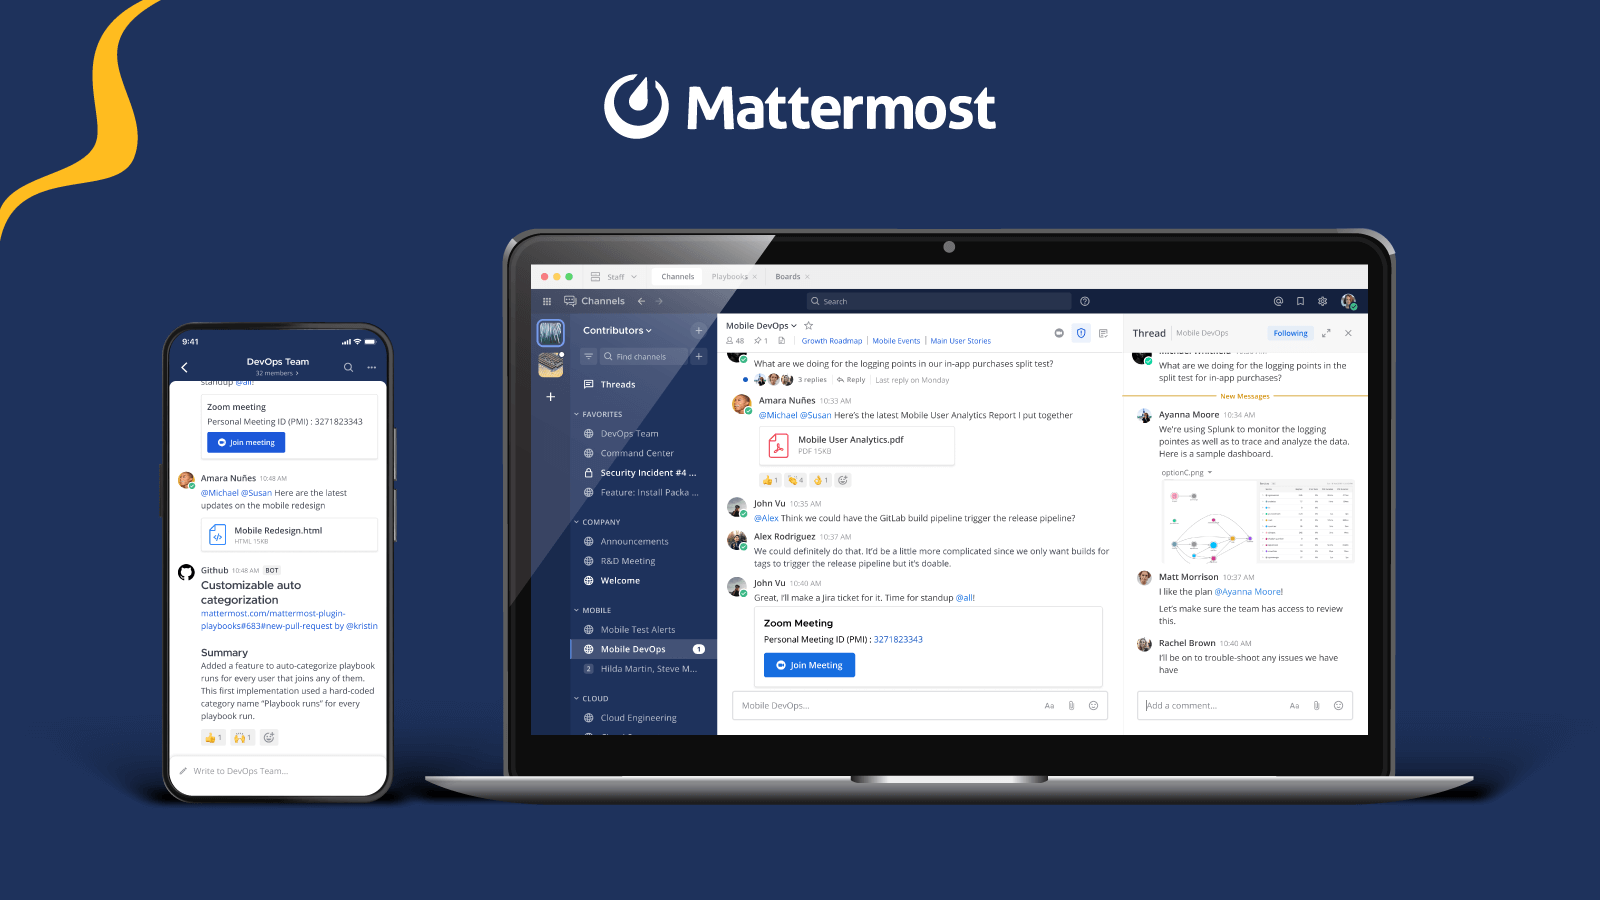
This is where Mattermost provides the operational coordination layer.
Mattermost enables organisations to bring secure collaboration, workflows and integrations into a sovereign environment that can support daily operations as well as incident response. The goal is not simply to create another place for teams to communicate, but to provide a trusted environment in which information can move from signal to action without losing context, control or accountability.
Trusted decision-making is the real outcome
Security controls are essential, but they are not the end goal.
The purpose of trusted connectivity and governed workflows is to help people make better decisions. Decision-makers need confidence that the information they are receiving is reliable enough to act on, that they understand where it came from, and that they have visibility into what has already happened.
They also need clear ownership and escalation paths, particularly when operating conditions become more demanding.
During an active incident, information may be incomplete and several teams may be working on different parts of the problem at once. Leaders may need to make consequential decisions before every question has been answered. In those circumstances, speed matters, but trusted context matters just as much.
That is where the relationship between devices, workflows and decisions becomes most important. Trusted devices enable secure connections. Trusted workflows preserve context and accountability. Together, they give decision-makers a stronger basis for action.
“When operating conditions change, the challenge is not simply keeping people connected. Teams need trusted information, shared context and clear decision authority so they can continue to act. That capability has to be built into how they work every day, not introduced for the first time during an incident.”
James Mullins, VP EMEA & APAC, Mattermost
Trust must hold as operating conditions change
A resilient operating environment should not work only under normal conditions. The same underlying trust model needs to hold as the organisation moves from routine activity into heightened pressure and, if necessary, active disruption.
Everyday operations
During normal operations, teams need secure access to the systems and workflows that support their work. They may be sharing threat intelligence, coordinating investigations, managing operational tasks or collaborating across organisational boundaries.
Here, trust supports efficiency as well as security. Known users and devices can access the right environments, information moves through established workflows, and teams can collaborate without giving up control over sensitive operational data.
This creates immediate value, but it also establishes the habits and operating structures that become important later.
Heightened pressure
As risk increases, the operating environment becomes more complex.
More teams may need access to the same information, escalations become faster, leadership needs more frequent updates, and external specialists or partners may need to participate. Trust becomes harder to maintain precisely because the environment is changing.
This is where established systems and workflows matter most. Teams should not need to redesign access controls, create new communications channels or work out who has authority to act while the situation is already developing.
The more of that structure is already in place, the easier it becomes to increase operational tempo without losing control.
Active disruption
During an active cyber incident, assumptions about the primary technology environment can change quickly.
Corporate communications may be compromised. Identity services may become unavailable or untrusted. Networks may be deliberately isolated as responders work to contain the breach. Teams can find themselves trying to coordinate precisely when the systems they normally depend on are no longer available.
This is where architectural independence matters.
An out-of-band communications environment should not share the same points of failure as the systems it is intended to replace. Mattermost can be deployed self-hosted, on-premises or within isolated environments, providing organisations with a sovereign operational channel that can function independently of compromised primary collaboration or cloud services.
For highly sensitive environments, that can include architectures designed for isolated or air-gapped operation, allowing authorised teams to continue communicating and coordinating without depending on the affected primary environment.
The organisation still needs to know who is participating, which devices are authorised, what information can be relied on and how decisions are being recorded. But it also needs confidence that the response channel itself remains under its control.
That is why resilience should not depend on switching to an improvised consumer application or an emergency service that shares the same infrastructure dependencies as the primary system. The fallback environment needs to be deliberately architected for independence, sovereignty and continuity.
The same trust principles should continue to apply as the organisation moves from everyday operations to heightened pressure and active disruption.
Resilience depends on how the layers work together
Most organisations already have multiple security controls in place. The challenge is that these can still function as isolated layers.
Secure identity without trusted workflows is incomplete. Secure messaging without confidence in the devices connecting into the environment is incomplete. Workflow automation without governance and auditability is incomplete. Incident communications that teams rarely use may also create friction at the moment they are needed most.
Operational resilience depends on how these layers combine.
It is therefore more useful to think about trust as a chain than as a collection of separate technologies. A weakness at one point can affect everything that follows. If a device cannot be trusted, the connection becomes questionable. If the workflow is unclear, information may not reach the right person. If decision-makers cannot establish context or provenance, they may hesitate to act.
Resilience comes from maintaining that chain from connection through to decision.
Building trust across the operational environment
Establishing trust from connection to decision requires different layers of the operational environment to work together.
Arqit’s quantum-safe symmetric key agreement helps establish cryptographic trust between authorised devices and supports organisations preparing for post-quantum security requirements.
Mattermost provides the sovereign operational environment in which those trusted participants coordinate, share information, execute workflows and make decisions. Because Mattermost can be deployed independently of an organisation’s primary collaboration environment, that same coordination layer can support everyday operations and remain available when primary systems are compromised or deliberately isolated.
Together, these capabilities support a broader model of operational trust spanning the device, the connection, the environment, the workflow and ultimately the decision.
The significance is not simply that two technologies can be deployed together. It is that trust established at the connection layer can be maintained through the operational workflows and decisions that depend on it, even as operating conditions change.
Trust is an operational capability
Trust should not be treated as a single control, certificate or security feature. It needs to be established and maintained across the entire operational environment, from the point a device connects to the moment a decision is made.
That means looking beyond individual technologies and asking whether the wider system of devices, connections, workflows and people can continue to operate with confidence as conditions change.
This question will be central to the conversation for Mattermost and Arqit at GovWare 2026 in Singapore. As government, financial services and Critical Information Infrastructure organisations examine how to strengthen resilience across increasingly distributed environments, the focus cannot stop at protecting individual systems. It must also include how trust is established across those systems and sustained through everyday operations, heightened pressure and active disruption.
The strongest operational environments are not simply secure. They are designed so that trust can persist from the devices participating in the environment, through the workflows that structure activity, to the decisions that determine what happens next.
That is what turns security into operational resilience.
Meet Mattermost and Arqit at GovWare 2026
Join Mattermost and Arqit at GovWare 2026, 13–15 October at Marina Bay Sands, Singapore. Visit us at Booth E36 to explore how quantum-safe device connectivity and sovereign operational coordination can help keep critical operations moving.