This is the second post in the Devices series. Part 1 covered Foundation-stage controls: managed deployment through AppConfig, ID-only push notifications, and integration with your existing MDM. This post covers the Advanced stage. For the identity policies it builds on, see the Identity series.
Enrollment is an event. Posture is a condition.
A device enrolled in your management platform in March tells you something about March. It tells you very little about the phone in an operator’s hand this morning. Programs that stop at enrollment are trusting a point in time.
The snapshot problem
Foundation controls reduce what can go wrong. They do not verify what is true.
The Advanced stage in this series moves from “trust the past” to “check the present.” Under the CISA Zero Trust Maturity Model (ZTMM), that is the shift from static device inventory toward continuous assessment in the Devices pillar. The DoD Zero Trust Strategy points the same way, and ACP 240 environments need the same property: access decisions that reflect current conditions.
Access is not control. A valid session on a managed device does not tell you who is holding it, what state it is in, or whether either has changed since sign-in.
Three questions define the stage: who holds the device, how is it managed, and what does it report right now?
Who holds the device
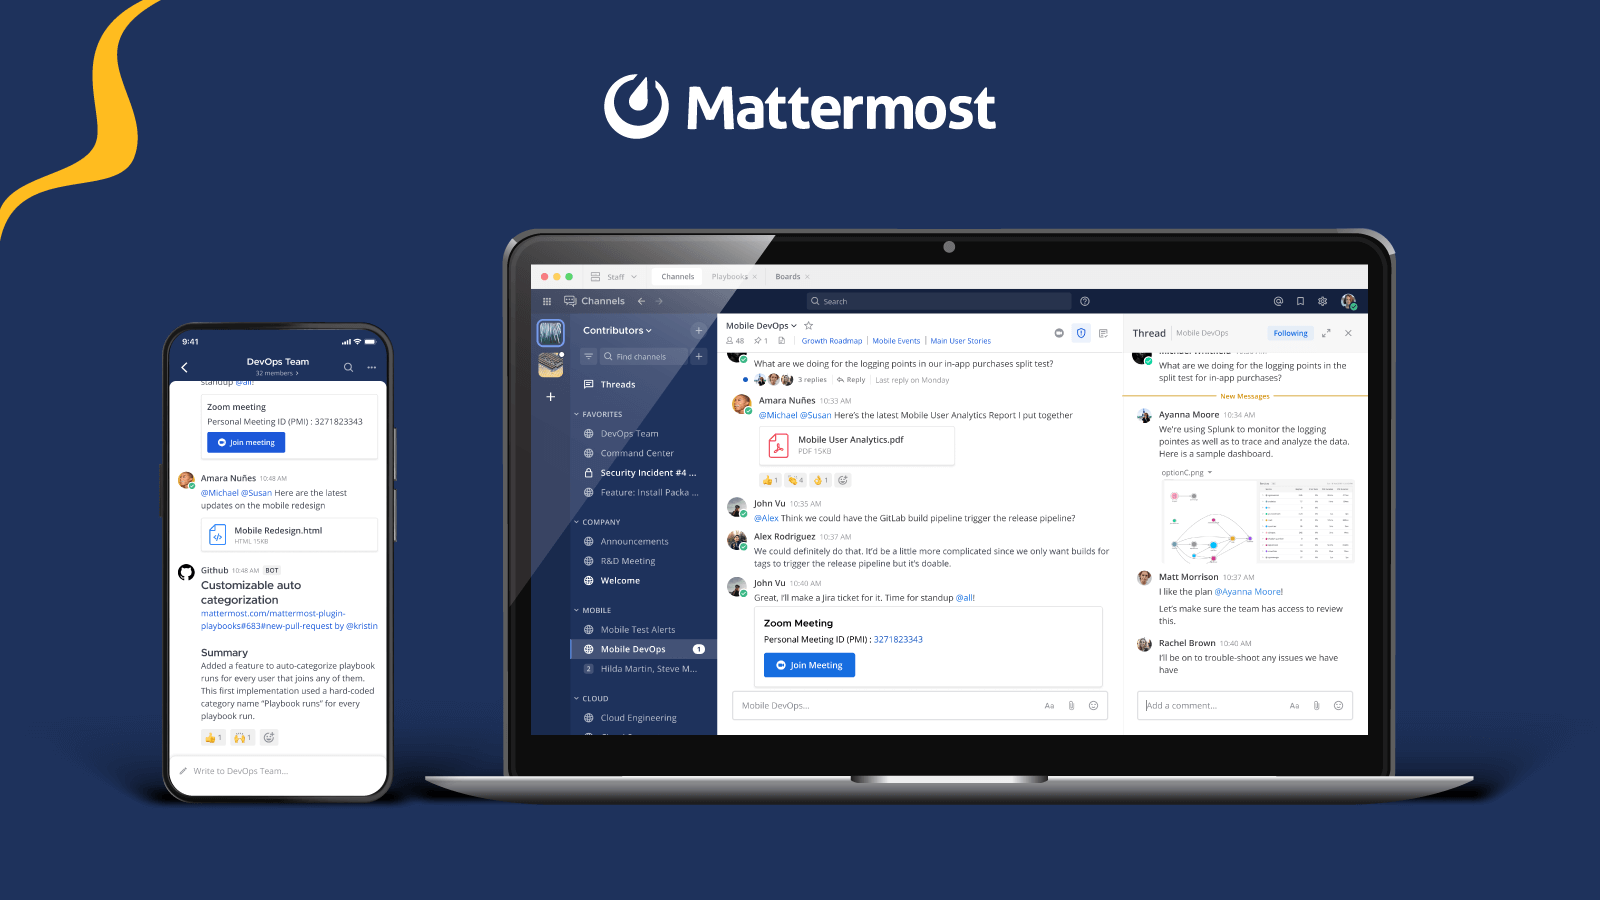
Mattermost mobile biometrics (Mattermost Enterprise Advanced edition) tie access to the app to a biometric check of the person holding the device. A stolen, borrowed, or left-behind phone does not carry a session with it.
Biometrics add friction, and operators will notice. Decide deliberately which roles and channels warrant it. A control that people route around becomes shadow IT, and shadow IT is a security failure.
How the device is managed
Many mobile programs run on Microsoft Intune. Mattermost works with that investment.
Intune MAM for iOS (Mattermost Enterprise Advanced edition) evaluates compliance continuously at runtime. If a device becomes non-compliant, your session reflects that change and access policies can evaluate your new posture automatically. No one has to file a ticket or wait for a sync.
Today this is iOS only. For Android, deployments use Android Enterprise work profiles. Plan the two platforms as two designs, not one.
The pattern matters more than the product name. Your management platform decides what compliance means. The application enforces that decision at the moment data is requested. That is the layered model: no single product delivers Zero Trust, and each layer should make the others more useful.
What the device reports right now
Management status is one input. Network and device type are others. Session attribute collection lets the mobile app report device, network, and management posture to the server. Two design choices deserve attention from a security architect:
- Values live in memory only. They are held in the server’s in-memory session cache, not written to a permanent store.
- Silence fails closed. If no fresh report arrives within the time-to-live (TTL) plus a grace period, the attribute is treated as absent, and any policy that requires it denies access.
The second choice carries the argument. A device that stops reporting does not keep its trust. It loses it.
The bridge back to identity
In the Identity series, attribute-based access control (ABAC) policies evaluated clearance, program affiliation, and directory data. Device posture belongs in the same policy engine.
Consider a policy of this shape: allow downloads only when the device is managed and the network is a corporate one. Identity says who. Device attributes say from what, and under what conditions. Neither is sufficient alone. This is why the Identity series and the Devices series are one program. A policy that checks the user and ignores the device repeats the original mistake with better paperwork.
Questions for your architecture review
- Where does compliance get enforced? If the verdict lives only in your MDM console, the application never acts on it.
- Which platforms do you actually run? iOS and Android need separate plans.
- What happens when a device stops reporting? Your policy should say deny, and your users should know why.
- Which roles justify biometric friction? Start where the data is most sensitive.
- Does one ABAC policy see both user and device? If not, you have two programs.
Advanced is not the finish line
Advanced posture checks tell you the device is in good standing. They cannot tell you it is untampered, and they cannot protect data on a phone that is lost or offline. Those are Optimal-stage problems, along with where mobile programs most often stall.
Part 3 covers all of it. For now, the principle for this stage: access reflects current reality.
Next: Stay tuned for the next blog in this series: “Part 3: The Roadmap to Optimal.” For capability mapping across maturity stages, see the Zero Trust with Mattermost guide.