This is the first post in the Zero Trust Devices series. The Identity series ran in three parts: Part 1 covered Foundation-stage controls, Part 2 covered Advanced identity, and Part 3 covered the road to Optimal. This series picks up where identity stops.
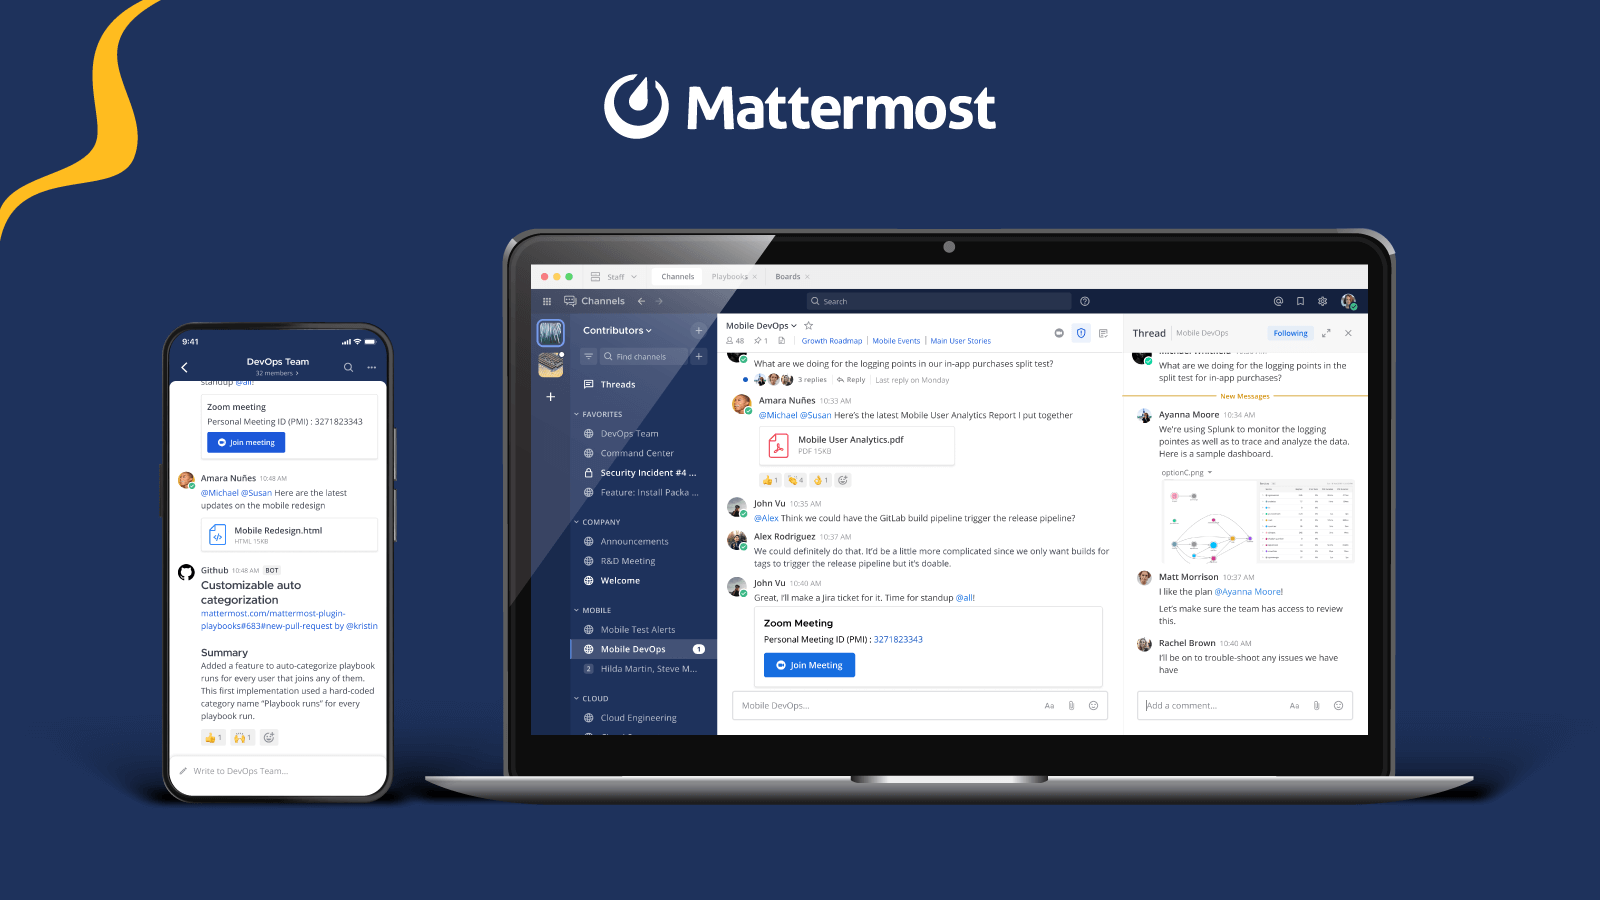
A cleared analyst signs in with valid credentials, clears multi-factor authentication, and opens an incident channel from a phone. The identity checks out. Nobody can say whether the phone does.
That gap is where the Identity series ended: a verified user on a compromised device is still a threat. The Devices pillar exists to close it.
Identity stops at the glass
Most Zero Trust programs still treat the device as a network problem. Put it on the right VPN, check a certificate, move on.
Mobile breaks that model. Phones roam across carrier networks, travel with their owners, and increasingly serve work and personal life at once. There is no edge to defend.
Leaders are being asked to extend Zero Trust to mobile and BYOD anyway. The DoD Zero Trust Strategy and CISA’s Zero Trust Maturity Model (ZTMM) each treat devices as their own pillar. ACP 240, for NATO and EU environments, frames access control around the data itself rather than the network that carries it.
Our position for this series is simple: Device integrity and posture has to be a condition of data access. Valid credentials do not make a device trustworthy.
Foundation: control the entry path and the leakage
In this series, Foundation is the first maturity stage, and it maps to the opening stage of the Devices pillar in CISA ZTMM and to the baseline device capabilities in the DoD strategy.
The Foundation does not require you to enroll every phone. Instead, it asks you to close two gaps you can already see: how the app gets onto the device, and what it could leak.
How the app arrives
A user who configures their own security settings has made a policy decision on your behalf.
Mattermost supports Enterprise Mobility Management (EMM) through AppConfig (Enterprise edition). Your EMM can push pre-configured server URLs, authentication settings, and data protection policies to the app. Users receive the configuration you reviewed and approved, not the one they remembered from the onboarding instructions.
This works without full device enrollment where mixed-use and BYOD phones may be a necessary tradeoff.
What leaks around the app
Push notifications are a subtle data path. They travel through Apple and Google notification services, which are well built for general use and sit outside your security boundary. The question is what you send through them.
ID-only push notifications (in Mattermost Enterprise edition) answer it. The notification carries an identifier, not the message. Apple and Google notification infrastructure never sees message content. This is operational sovereignty at the smallest scale: you decide what crosses the boundaries you do not operate.
What your EMM already knows
You have likely invested in an EMM or MDM stack, and effective controls should combine with it, not bypass or reimplement it. Mattermost integrates with MDM remote wipe and compliance policy, so a device your management platform flags can be acted on through the controls you already run. The right collaboration platform makes the rest of your stack more effective instead of asking you to replace it.
Four questions for your next mobile review
Take these to your security architect and your mobility lead.
- Who configures the app? If users do, your policy is a suggestion.
- What do notifications reveal? Name every service a message preview touches.
- Does the collaboration app know what your EMM knows? A compliance verdict that never reaches the application protects nothing.
- What is your plan for phones you don’t enroll? BYOD is already in your environment. Controls that require full enrollment will not reach it.
If any answer is “we haven’t looked,” that is your first sprint.
What Foundation does and doesn’t do
Foundation narrows exposure. It does not tell you the state of the device at the moment of access.
A phone can be correctly configured on Monday and compromised by Friday. Knowing the difference requires checking who holds the device, how it is managed, and what its posture reports right now. That is the Advanced stage.
Part 2 covers biometrics, Intune MAM on iOS, and live posture reporting. It also connects device attributes to the same attribute-based access control (ABAC) policies you built in the Identity series, so a decision about a user can finally account for the device in their hand.
The first principle of a data-centric Zero Trust program holds at every stage: protect the data wherever it lives. On mobile, it lives on a device you may never fully own.
Next: Stay tuned for the next blog in this series: “Part 2: From Enrolled to Verified.” To see how these controls map across maturity stages, read the Zero Trust with Mattermost guide.