Mattermost v11.11 gives content reviewers a fast, transparent way to understand who may have seen a flagged post with the new post exposure radius report feature. The team is heads-down on Mattermost v12.0, shipping in October 2026 with a large set of new capabilities and breaking changes worth planning for.
Read on for what’s new, or upgrade your Mattermost server to get started.
Data Spillage: Exposure Radius Report
Mattermost Enterprise Advanced
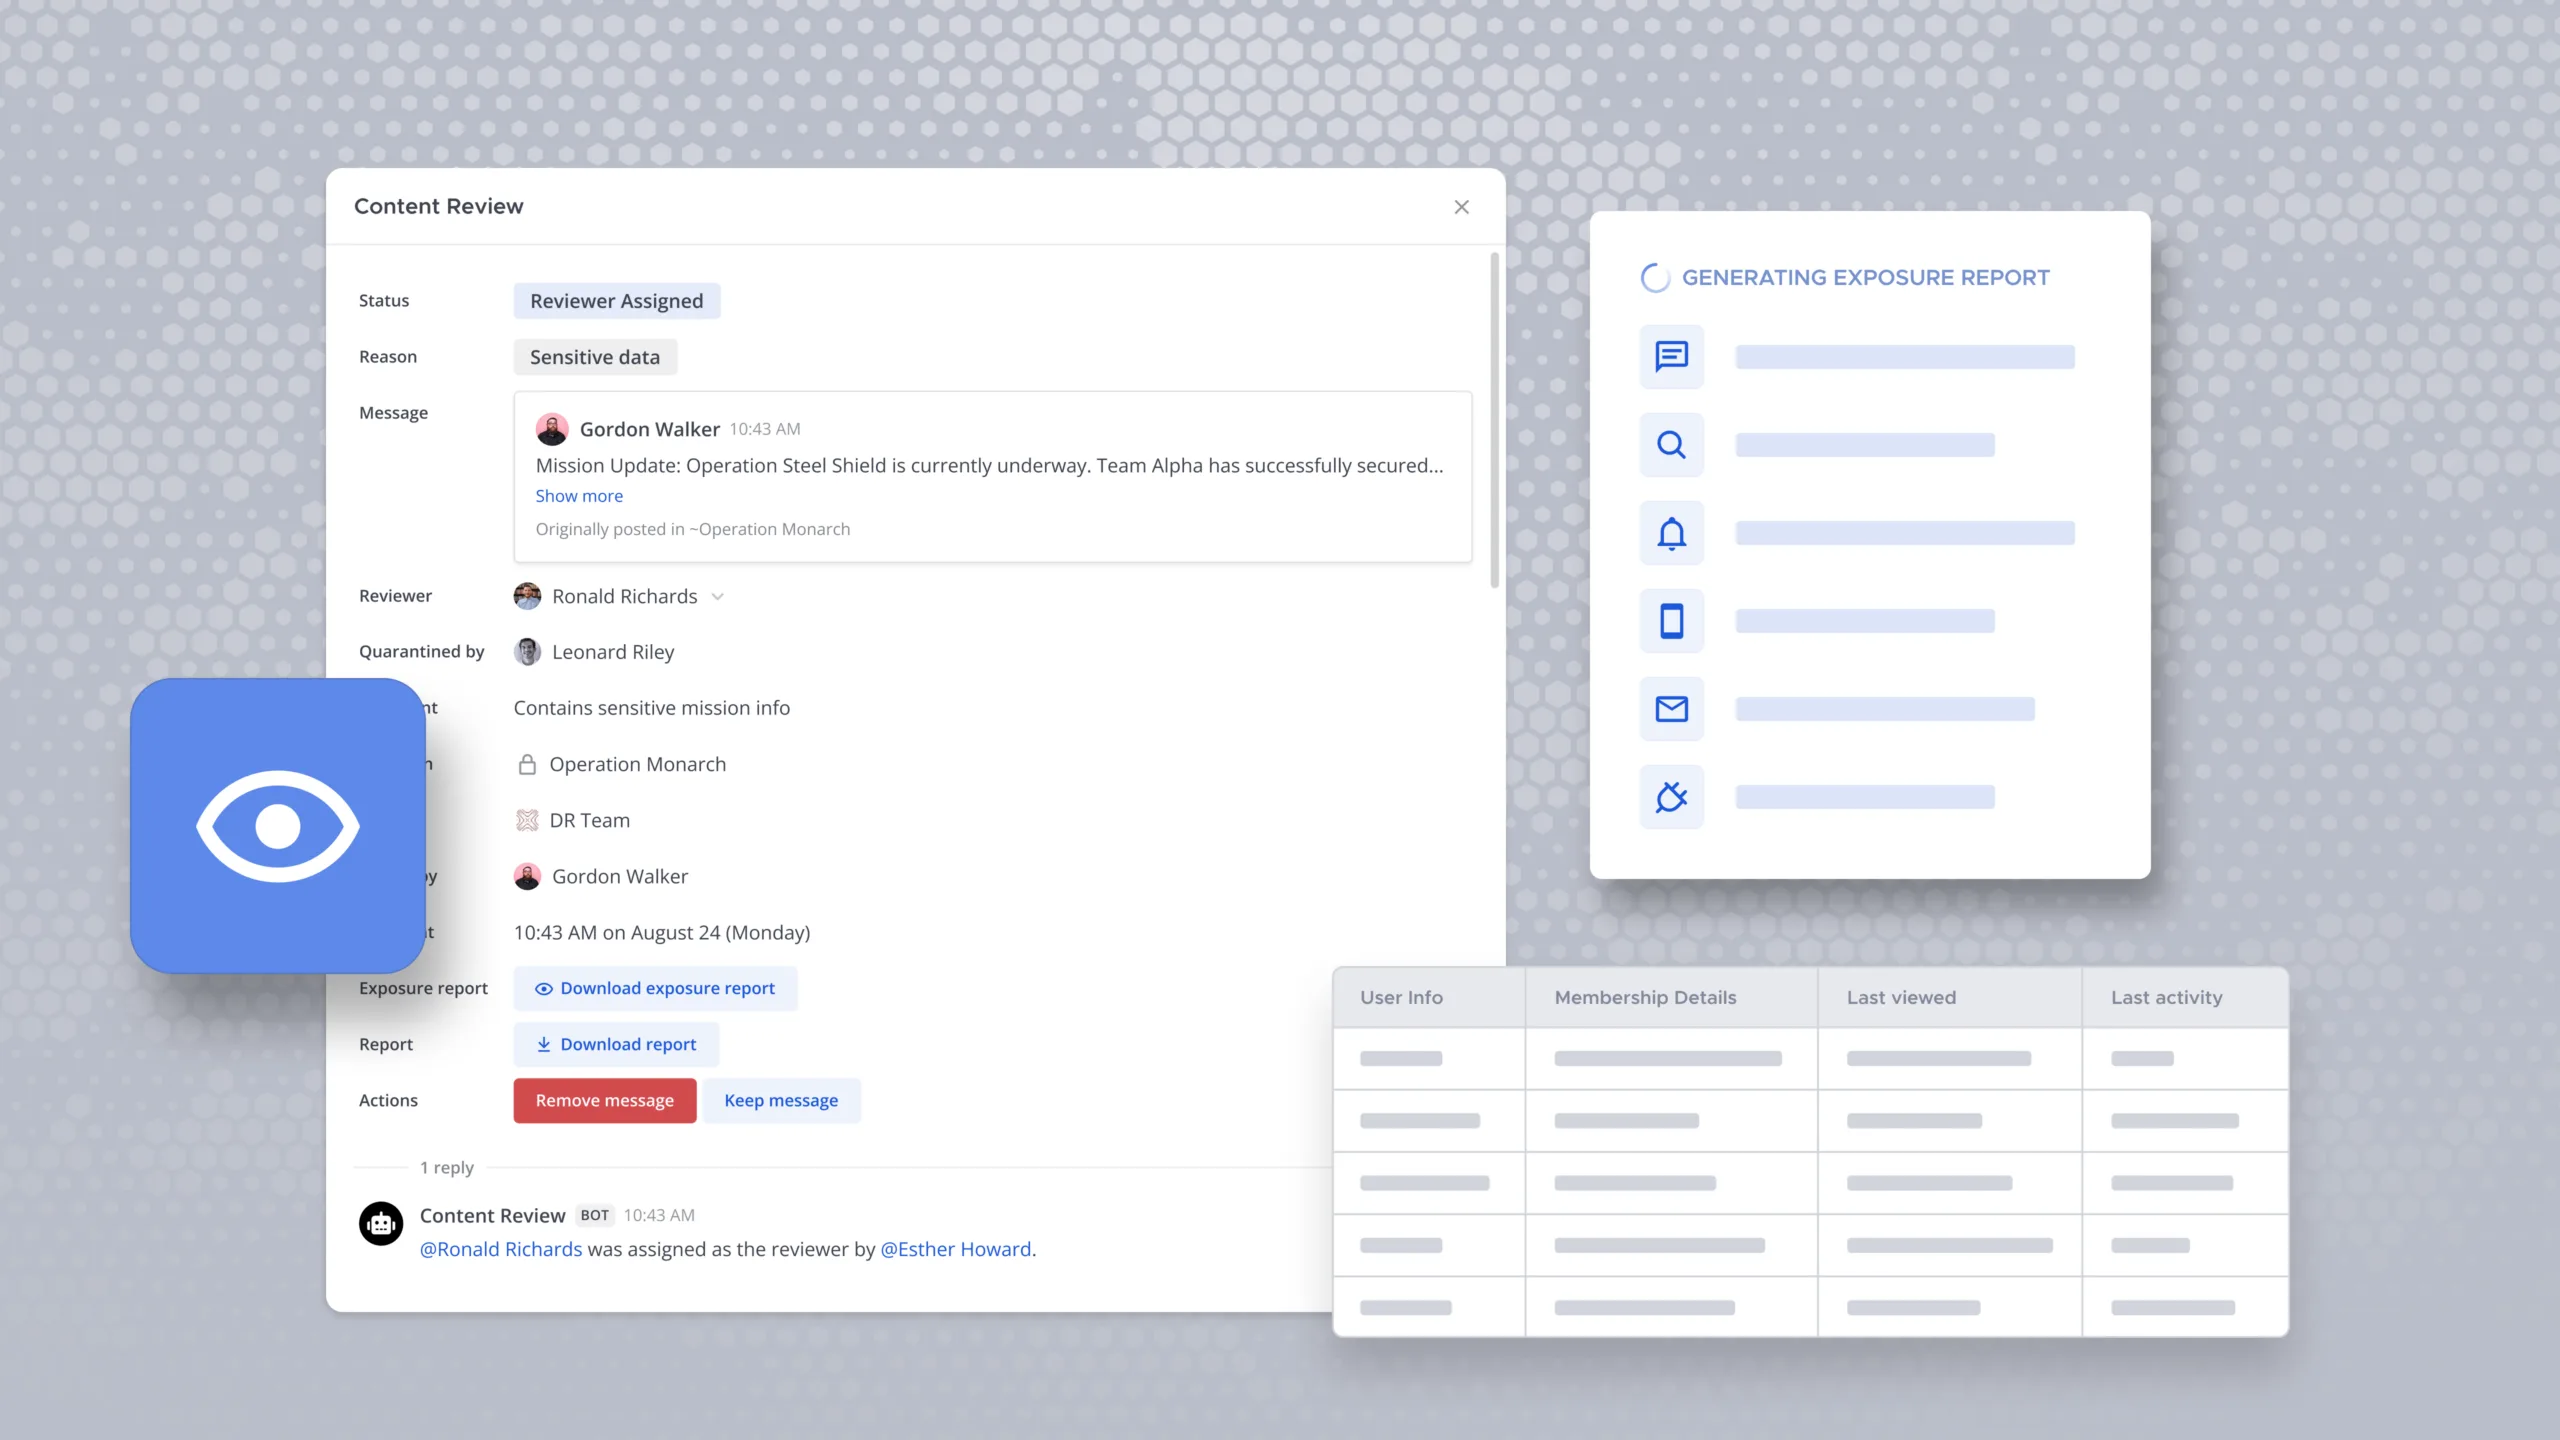
Mattermost’s Data Spillage Handling gives teams a built-in workflow for flagging, reviewing, and removing posts that may contain sensitive or regulated information, with notifications, an auditable review queue, and downloadable reports built in. The exposure radius report, new in Mattermost v11.11, extends that workflow with a next first step: understanding who may have already seen a flagged post.
When a post gets flagged for review, knowing who may have already seen it is time-sensitive. Doing it well requires tracing channel membership, activity windows, and notification paths. That’s a meaningful investigation, and speed matters.
With Mattermost v11.11, reviewers can now generate post exposure radius reports directly from flagged posts. These reports draw on channel membership history and each user’s last activity to compile a list of people who might have seen the post — for example, anyone who was a member of the channel between when the post was made and when it was flagged, along with when they last viewed the channel.
Reviewers can generate full reports or just exposure radius reports on their own, and the feature works retroactively, so it can be applied to posts flagged before this release as well. To keep the process accountable, downloading a report notifies all content reviewers, so exposure checks can’t happen quietly even if the flagged message is later removed.
The result is that reviewers get a fast, transparent first step toward understanding who might’ve seen a flagged post without having to wait on a manual investigation.
Learn more about Data Spillage Handling in Mattermost.
Mattermost Server: Upcoming Breaking Change
FIPS deployments enforce strict key-length requirements, and the updated glibc-openssl-fips bundle tightens that further, aligning with OpenSSL’s FIPS minimum of 112 bits for HMAC operations. Before updating to v11.7.10, v11.10.1, or v11.11.0, FIPS teams should confirm the password in SqlSettings.DataSource is at least 14 characters and rotate it in PostgreSQL if not. Standard non-FIPS builds are unaffected. This is a one-time check that keeps your upgrade path clean.
Learn more about v12.0 deprecations and breaking changes.
Desktop App: Upcoming Breaking Change
Teams running Mattermost with a subpath in their Site URL have one action item ahead of Desktop App v6.4 (November 2026): update the Boards plugin to v9.4.0 or later. This can be done from the Marketplace without a server update. Deployments without a subpath are unaffected, and taking care of this now means the v6.4 update lands without interruption.
Learn more about v12.0 deprecations and breaking changes.
Try Mattermost v11.11 today
Upgrade your Mattermost server to start using these new capabilities.
For a complete list of updates and improvements included in this release, visit the Mattermost v11 Changelog.