Zero Trust in Practice: Identity, Part 3 — The Roadmap to Optimal
This is the third part in the Identity series. Part 1 covered Foundation-stage controls: federated identity, MFA, directory sync, and audit logging. Part 2 covered Advanced identity: ABAC, dynamic policy evaluation, and continuous access enforcement. This post covers the Optimal maturity stage and how to actually get there.
What Optimal identity looks like
The Advanced stage gets you continuous, attribute-based access control evaluated against synced directory data. That’s a significant leap from static roles. But it still has a dependency: attributes are updated on a synchronization cycle. The access decision reflects the last sync, not the current moment.
For most organizations, that’s fine. A sync cycle measured in minutes is close enough to real time for the vast majority of access decisions.
But for some environments, it isn’t. Classified operations, real-time clearance adjudications, and mission-critical access decisions can’t tolerate even a short window where a revoked clearance still grants access or a missing attribute blocks an operator from their mission.
In those environments, the sync lag is a security or operational gap. Optimal identity maturity closes those gaps entirely.
At the Optimal stage, access is evaluated in real time against authoritative sources. There aren’t any cached attributes or sync dependencies, and trust isn’t assumed to persist between sessions.
How Mattermost reaches Optimal
Two capabilities define Optimal identity maturity in Mattermost.
1. Dynamic ABAC from multiple authoritative sources
At the Advanced stage, ABAC policies evaluate attributes synchronized from a single directory — typically AD/LDAP. At Optimal, dynamic attribute-based access controls (ABAC) pull from multiple authoritative sources simultaneously: clearance systems, HR platforms, program management databases, and identity stores can all feed into a single policy evaluation.
This matters because real organizational identity is rarely housed in one system. Clearance level lives in one place, program affiliation lives in another, and device enrollment status lives in a third. Optimal maturity means all of those sources contribute to the access decision, evaluated together, in real time, every time.
The practical effect: manual role management disappears entirely. There’s nothing to manage because there aren’t any static assignments. Access is a continuous output of policy evaluation against live data.
2. The User Authoritative Source interface
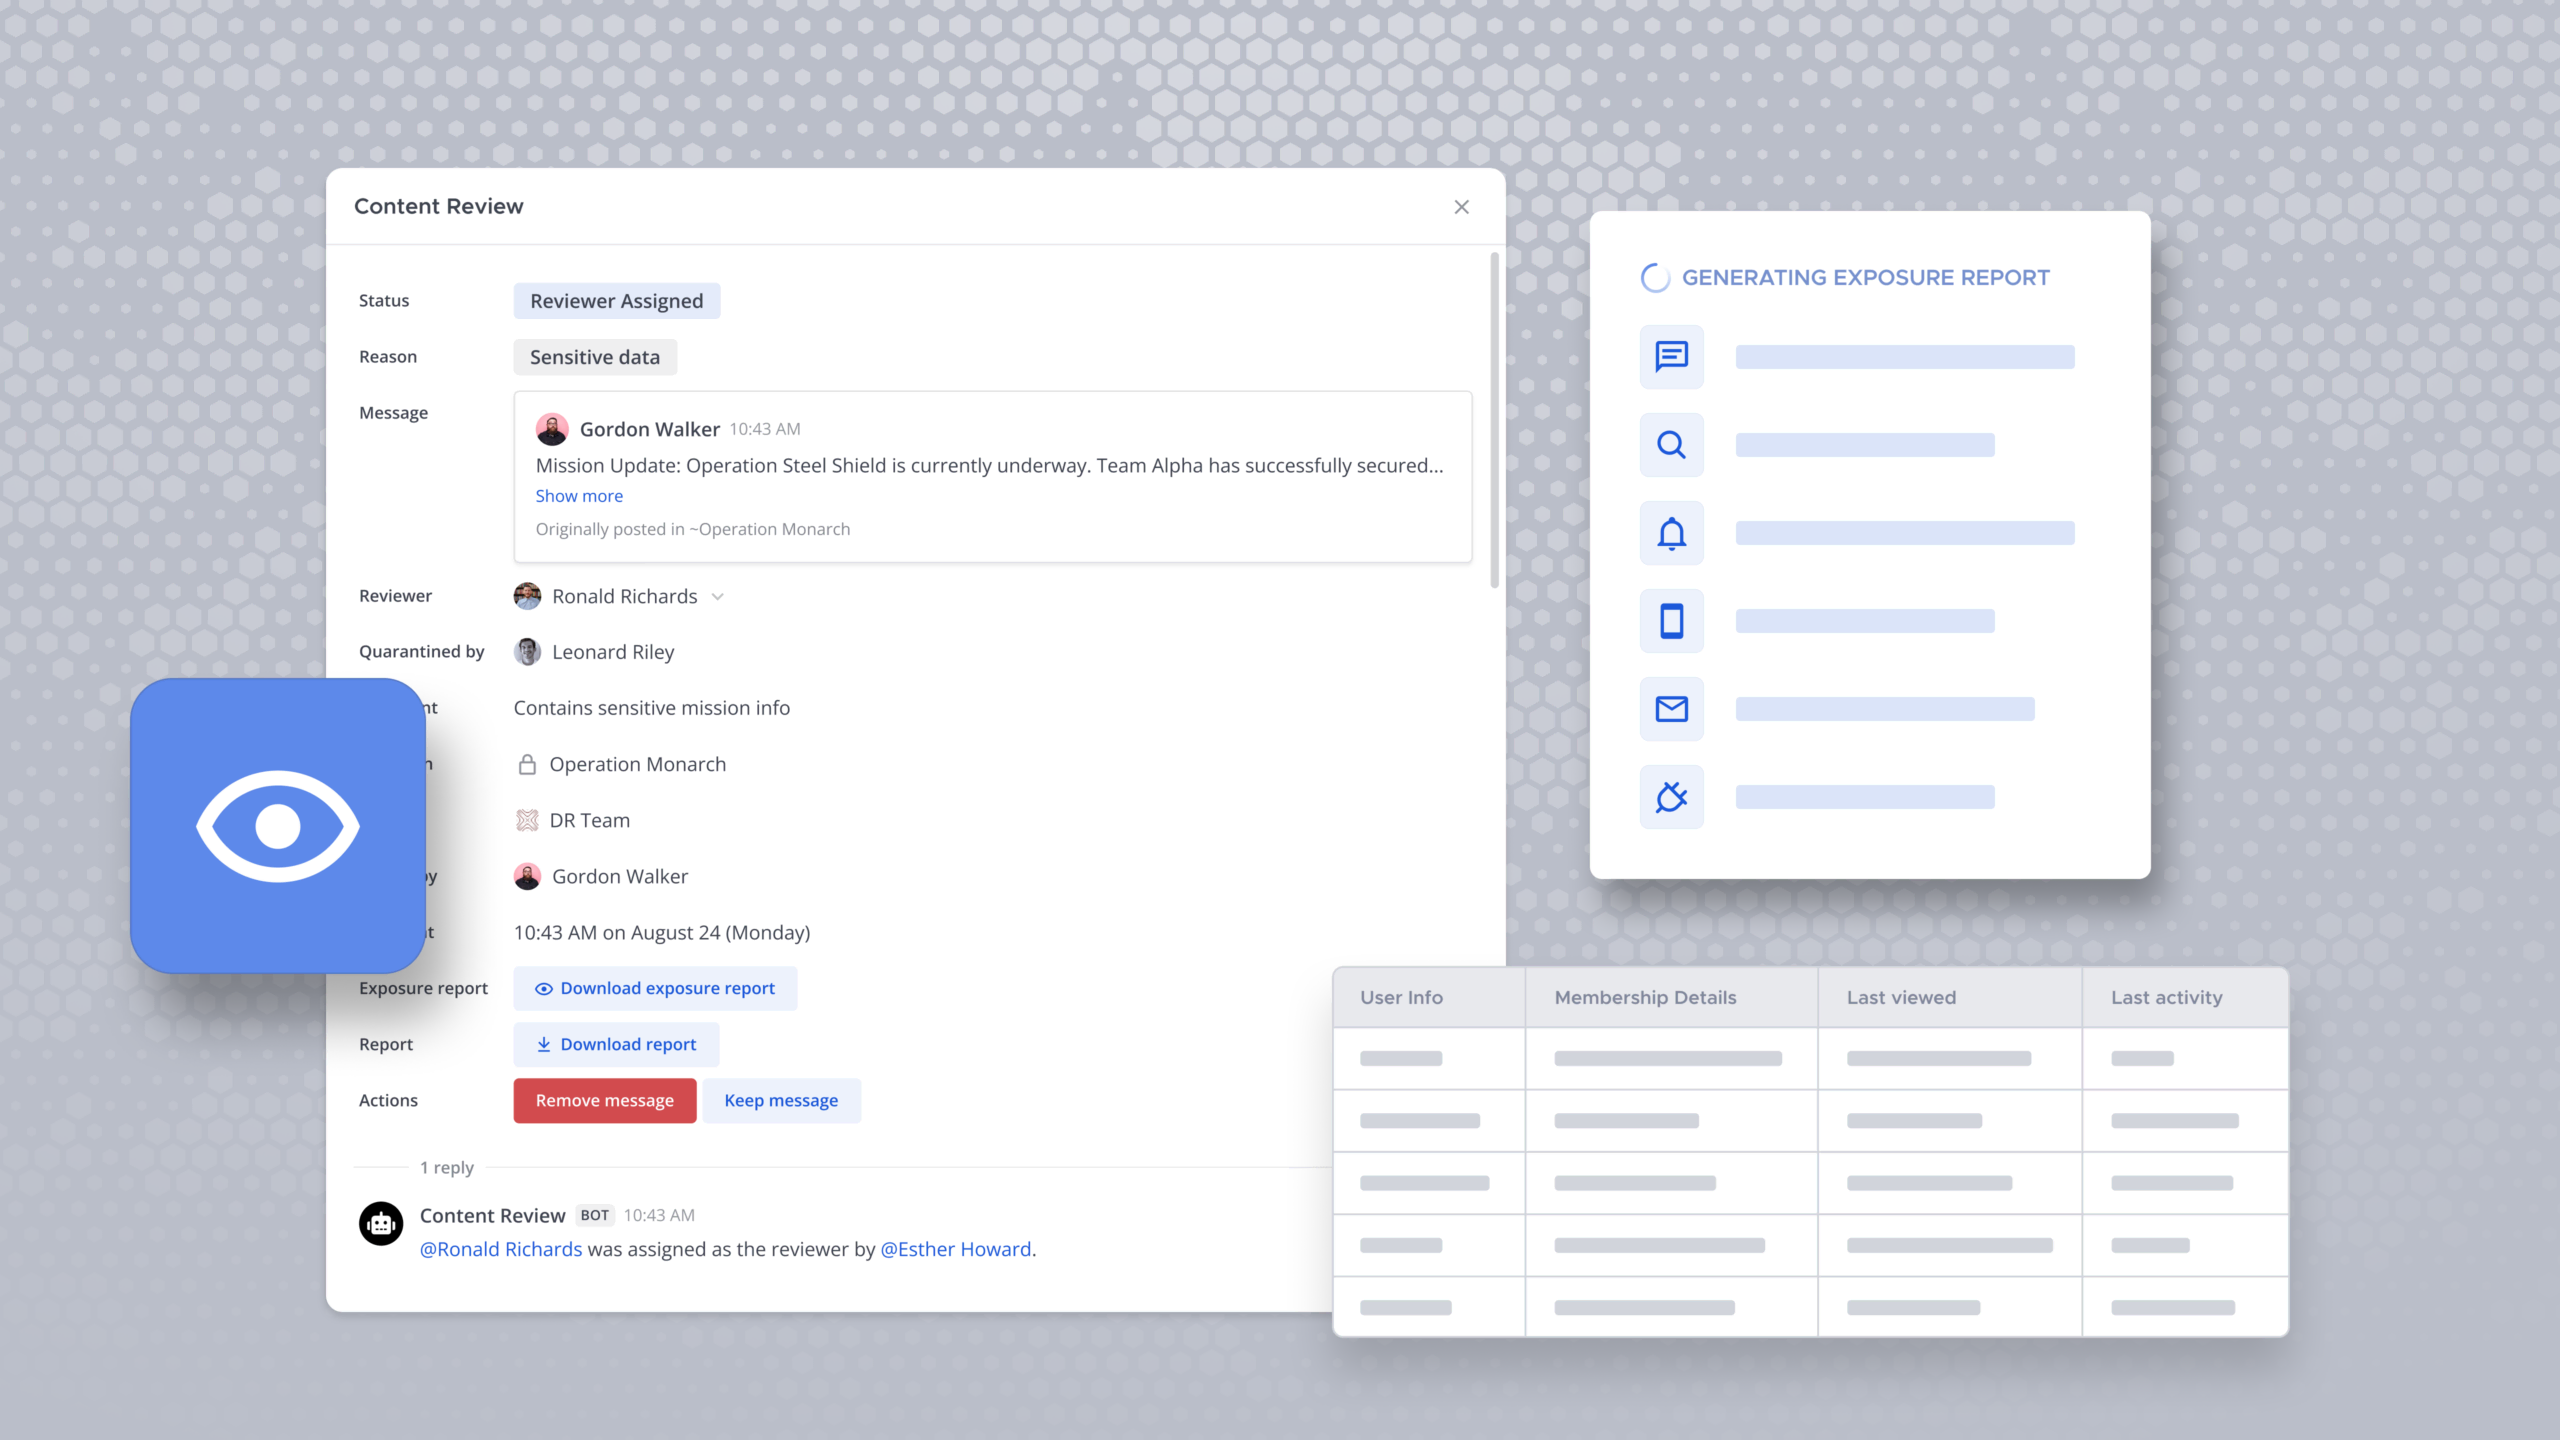
For government organizations operating a secure User Authoritative Source system, Mattermost provides a dedicated interface that queries individual clearances on demand rather than storing them locally.
This is a meaningful architectural shift. In Advanced ABAC, clearance attributes are synced to Mattermost and stored; the evaluation is fast, but the data is a copy. In Optimal ABAC, Mattermost reaches out to the authoritative source at the moment of access and asks: “is this clearance currently valid?” The answer comes back live.
The security implication is significant: a clearance revoked at 9:00 am is enforced at 9:00 am, not at the next sync or after someone files a ticket. Immediately.
The roadmap: where organizations actually get stuck
The Optimal stage is well-defined. The path to it is where most organizations run into trouble. In practice, three problems come up consistently.
1. The attribute population problem
ABAC policies are only as good as the attributes they evaluate. This sounds obvious, but the implication catches organizations off guard: before you can enforce a policy that evaluates clearance level and program affiliation, those attributes need to exist somewhere Mattermost can read them consistently, accurately, and continuously.
Most organizations discover that their authoritative data is messier than they thought. Clearance levels live in a spreadsheet someone updates quarterly. Program affiliations are tracked in a project management tool with no API. Organizational unit data in the user directory is two reorgs out of date.
The technical work of deploying ABAC is straightforward. The organizational work of cleaning up and connecting authoritative attribute sources is where the real effort goes and where timelines can slip.
The practical advice: start the attribute source audit before you start the ABAC deployment. Map where each attribute you want to evaluate actually lives, how current it is, and whether it’s accessible programmatically. That work determines your realistic timeline more than anything else.
2. The policy design problem
Mattermost uses Common Expression Language (CEL) to define access policies, a straightforward syntax for writing precise, readable access rules. CEL is flexible enough to express almost any access policy. That flexibility is also a trap. Organizations that start with “let’s model our existing access controls in ABAC” end up with policies that are just as complex and brittle as the role sprawl they were trying to replace.
The better approach: start with the most critical access restrictions and work backwards. What are the three or four conditions that should always gate access to your most sensitive channels? Write those policies first, deploy them, and learn from how they behave in practice before adding complexity.
ABAC done well simplifies access management. ABAC done poorly just moves the complexity from role assignments to policy expressions.
3. The organizational alignment problem
Dynamic ABAC that automatically adds and removes channel members based on attributes touches people — real users who notice when their access changes. Without clear communication about why a user’s access has changed, automatic removals feel arbitrary and likely to generate support tickets.
The organizations that deploy ABAC smoothly treat it as a change management exercise. They communicate the model to users before it goes live, give users a clear path to request access review if they believe a policy is wrong, and designate an owner for policy governance: someone who can evaluate whether a policy is working as intended and adjust it when organizational reality changes.
A realistic maturity timeline
So how long does a Zero Trust implementation actually take? The honest answer is: longer than most organizations plan for.
Gartner predicts that only 10% of large enterprises will have a mature and measurable Zero Trust program in place by the end of the year, up from less than 1% in 2022. The firm also expects that 75% of U.S. federal agencies will fail to meet Zero Trust requirements through 2026 due to a lack of funding and expertise.
The DoD, with its 2027 adoption mandate, treats Zero Trust as a multi-year program. That’s a helpful benchmark: this is years of work, not quarters.
For the identity pillar specifically, your time is determined by the three variables discussed above: attribute source readiness, policy complexity, and organizational change management. If you have clean authoritative data and a focused policy scope, you’re at the faster end. If you have fragmented attribute sources and complex legacy access models, you’re at the slower end.
The honest framing for leadership: Foundation and Advanced deliver real security value on their own. Optimal is the ceiling, not the prerequisite. Every step you move closer to Zero Trust reduces your exposure. Ultimately, the direction matters more than how fast you get there.
Closing the identity series
Identity is the highest-leverage Zero Trust pillar because it’s the one that governs every other access decision. Getting it right, from Foundation through Optimal, is the prerequisite for everything else.
But identity alone isn’t enough. A verified user on a compromised device is still a threat. A clean identity posture with no visibility into device health leaves a significant gap in the access decision.
Stay tuned: The next series covers the Devices pillar: how Zero Trust applies to endpoints and mobile, what device posture actually means in practice, and how Mattermost enforces device-level controls as a condition of data access, not just network access.
If you’re ready to assess where your organization sits across the Zero Trust maturity stages or you’d like to talk through your specific environment, contact a Mattermost Zero Trust expert today.
Mattermost Enterprise Advanced supports Optimal identity maturity through Dynamic ABAC and the User Authoritative Source interface. For a full technical capability mapping, see the Zero Trust with Mattermost documentation.