Consider a watch officer who needs to pass a reporting update to a partner team on a higher-classification network. The update is the most valuable thing in the room. It is also the hardest to move. So someone prints it, walks it to another building, scans it, and waits. By the time it lands, the moment it was meant to inform may have passed.
The most valuable information carries the tightest rules
The information that matters most to a mission almost always has the strictest handling requirements and an expiration date. Sensitivity and importance rise together, and so do the controls around them. That is as it should be. Unfortunately, the cost is speed.
When the approved path is slow, teams fall back on manual steps. Manual steps are only as reliable as the people following them, and they leave a thinner record than a system would. The goal is to get the right information to the right people, and only the right people, without giving up either speed or control. Two flows decide whether that works.
Low to high and high to high
Low to high moves information from a lower-classification domain into a higher one. Think of a field team analyzing public news reports and sending reporting up to the analysts who fuse it with everything else they hold. This flow drives decisions and it only works if what enters the higher domain is inspected, permitted, and not malicious.
High to high moves information between two domains at the same level, such as separate agencies or allied partners, each with its own governance. A matching classification level does not inherently grant a Need-to-know. The recipients on the far side have to be only the people who should see it, and that depends on more than clearance. Program affiliation, role, and device and network posture all play a part.
Both flows ask the same question of the system: who is allowed to receive this, and how do you know?
Cross Guard gives collaboration a managed path
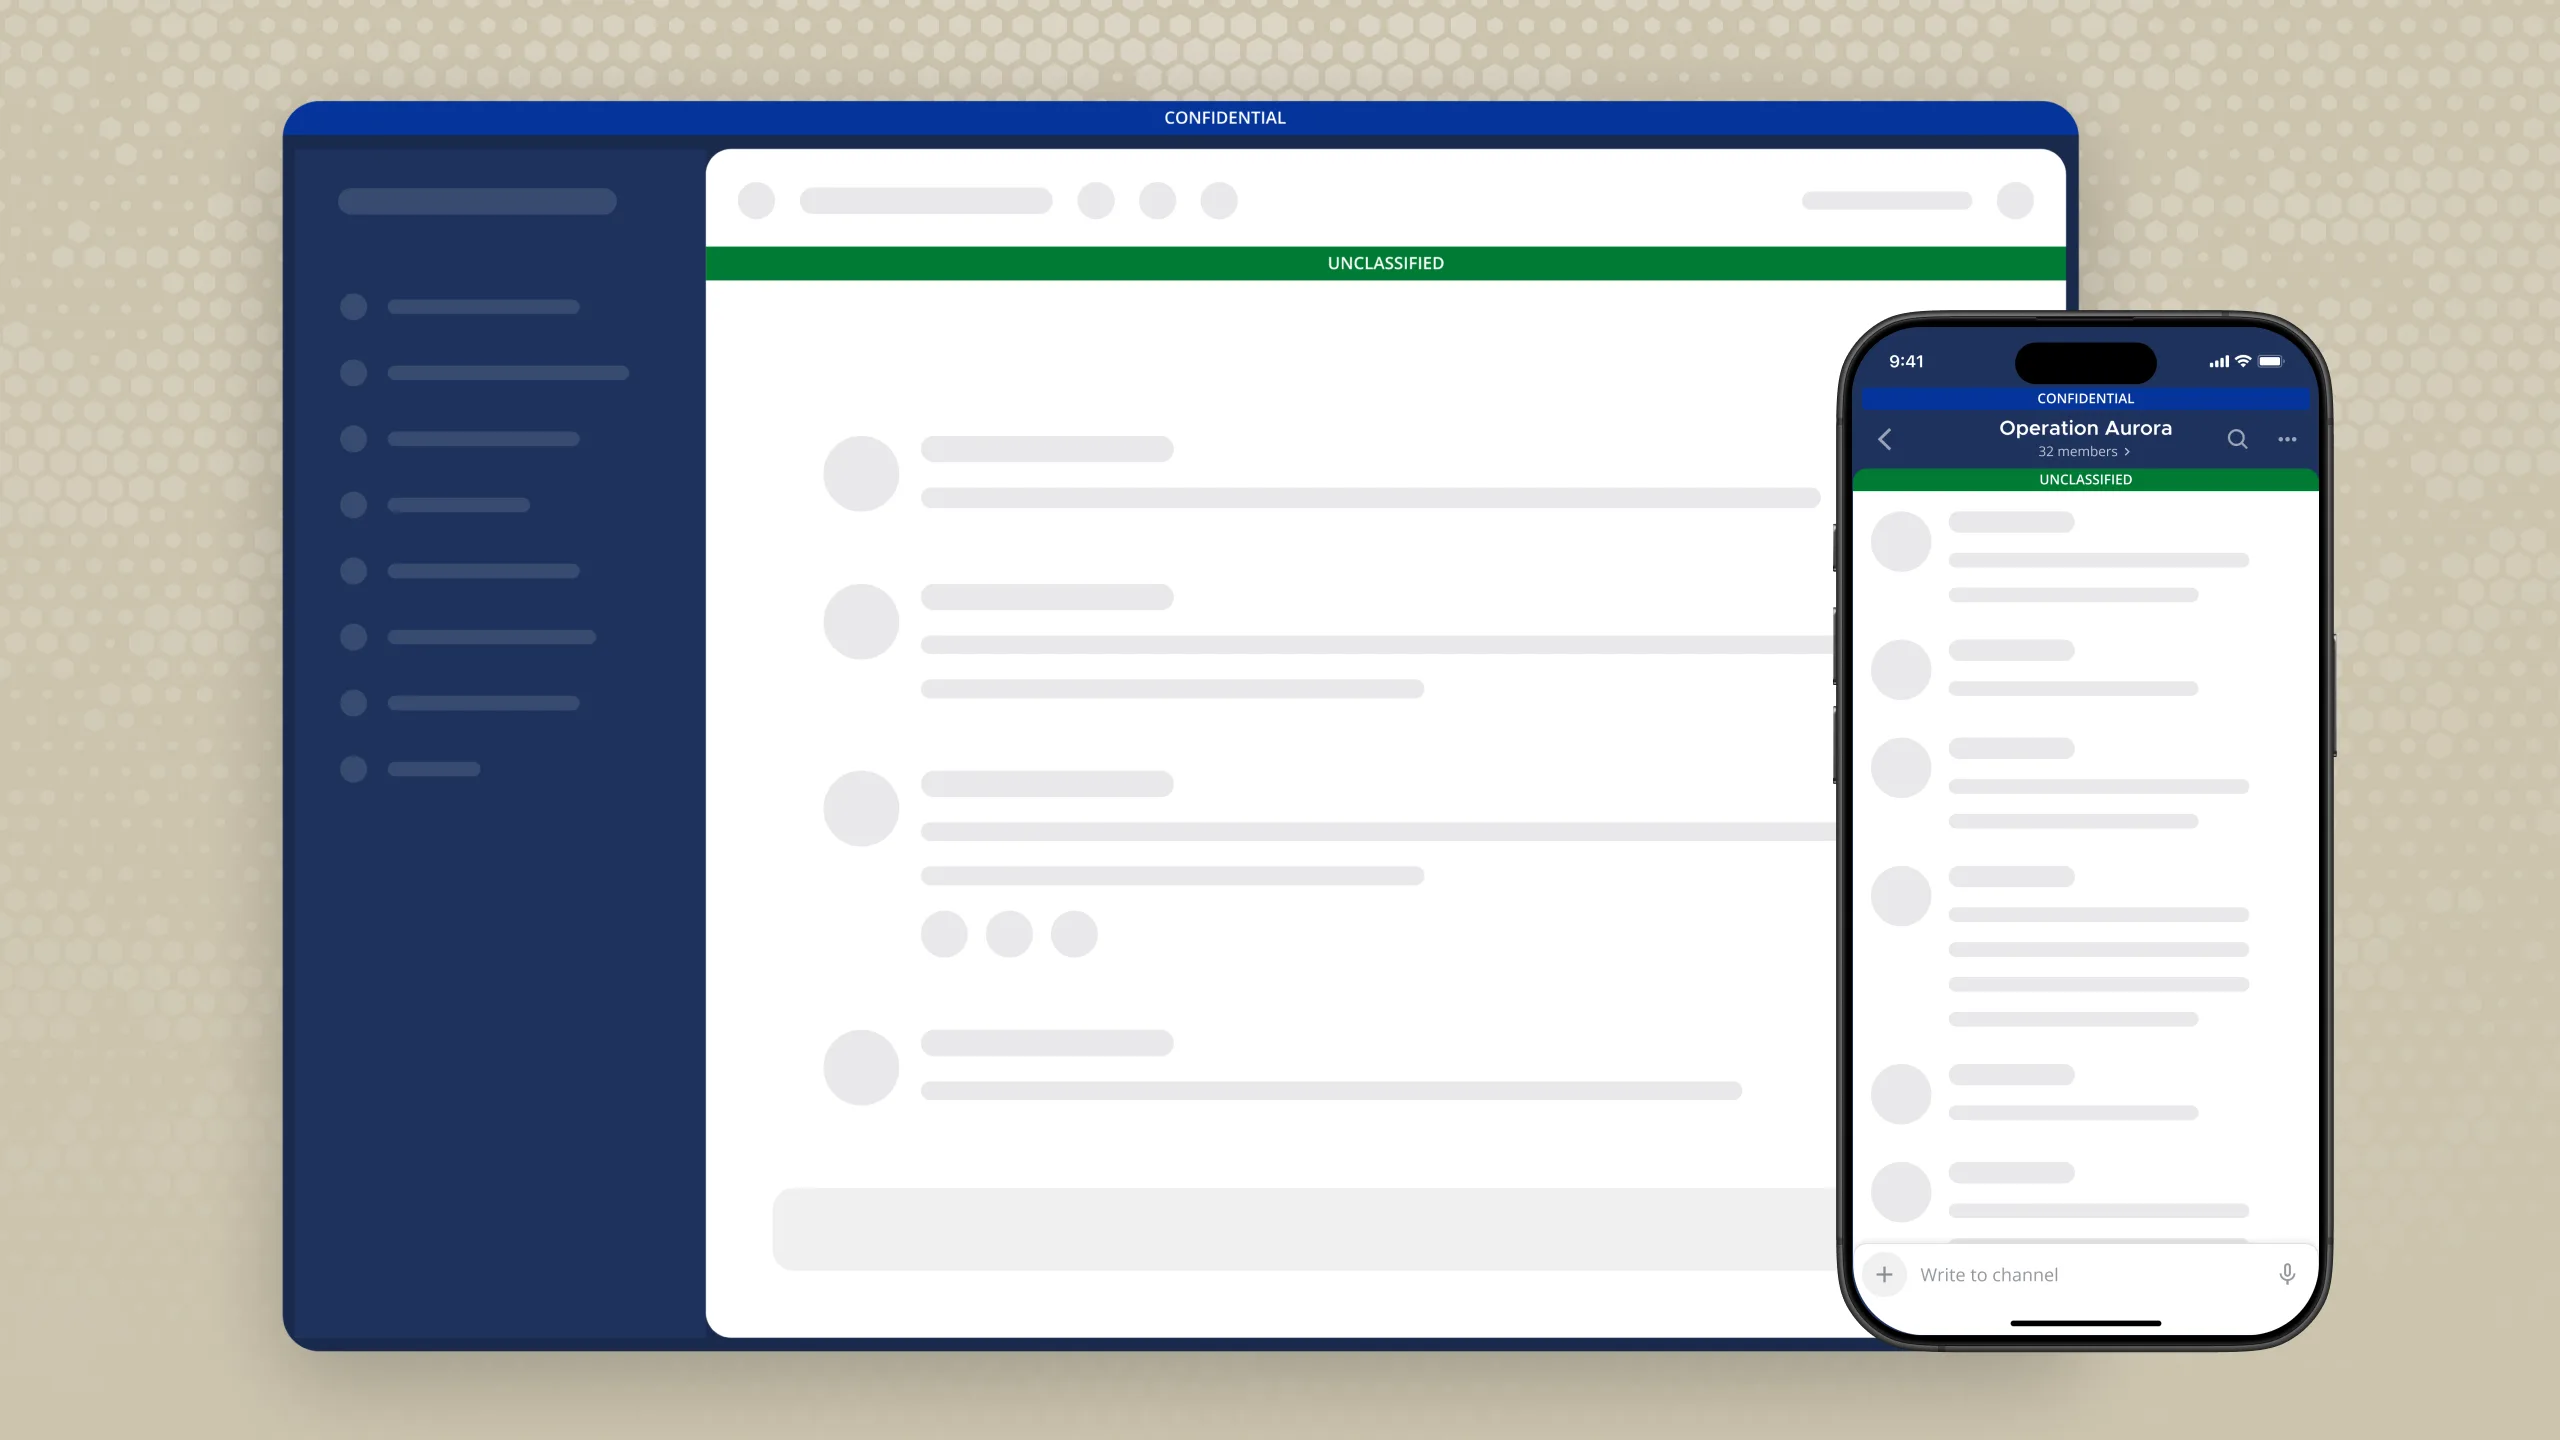
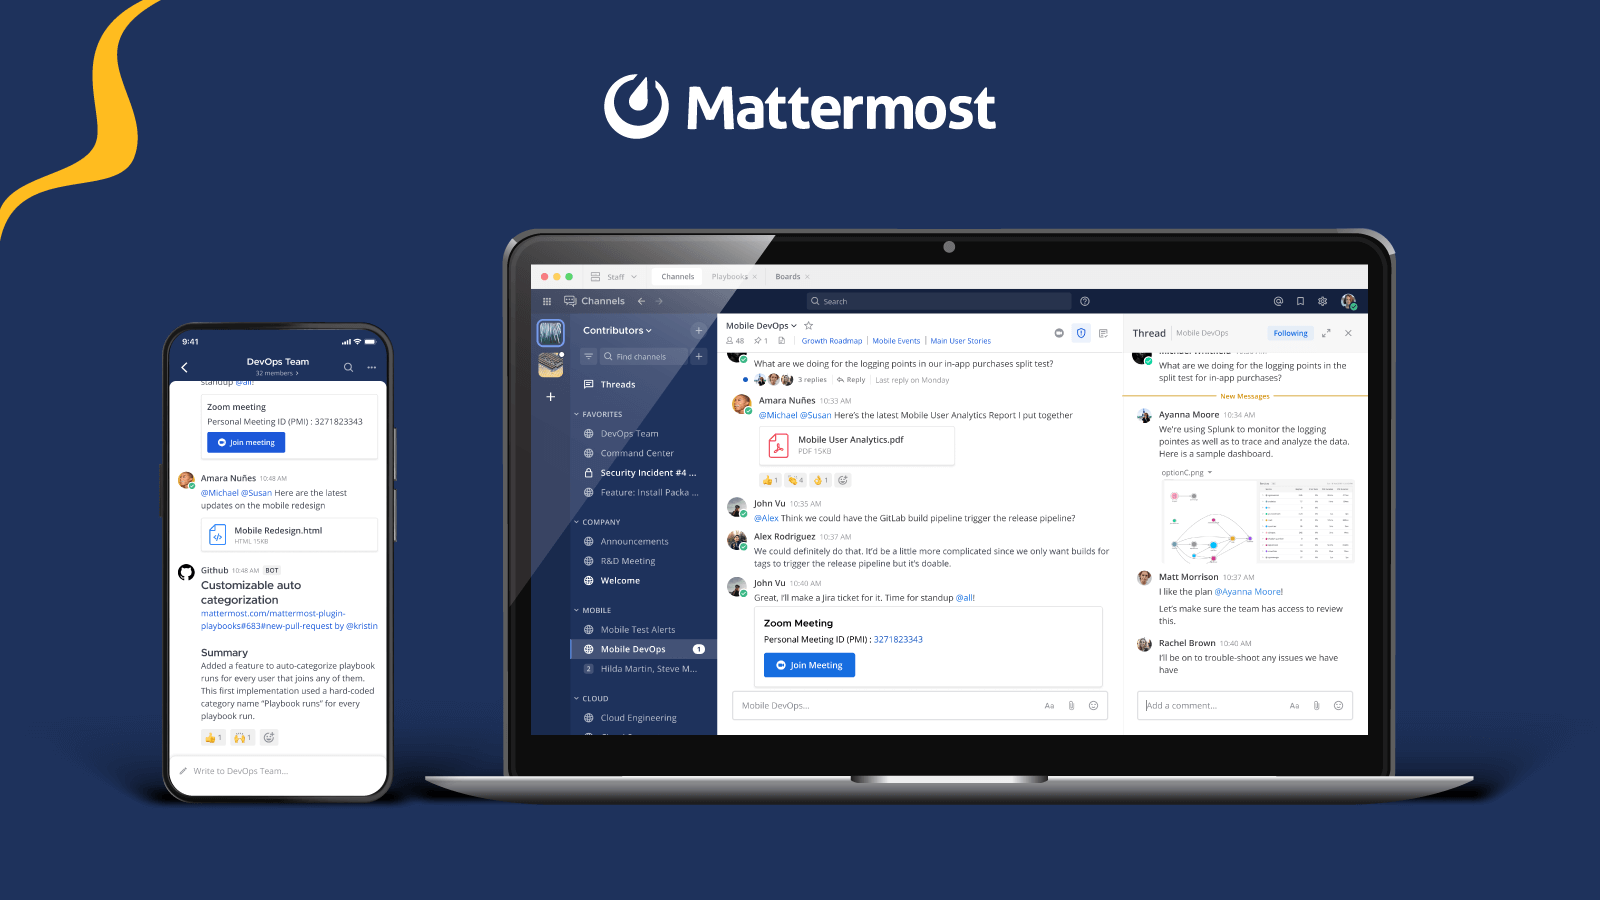
Cross Guard, built in collaboration with infodas, is a Mattermost plugin that federates channel messaging across classification boundaries through customer-accredited Cross Domain Solutions. infodas brings cross-domain expertise: its Secure Domain Transition (SDoT) product family inspects, filters, and transfers sensitive information according to strict security policies. Mattermost supplies the place where operators work on both sides.
The limits are worth stating plainly. Cross Guard works within the Cross Domain Solution your organization has already accredited. It does not replace that infrastructure or the accreditation work behind it.
Collaboration with governance and audit attached
The result is collaboration that carries its governance with it. A transfer is a post in a channel, so it lands in the same record as the conversation around it. A named person made the decision, and an auditor can reconstruct what moved, between which domains, and under which policy.
Compare that with the printed page. A walked document leaves a trail of signatures, if everyone follows procedure. A governed transfer leaves a record by design.
Cross Guard with attribute-based policies
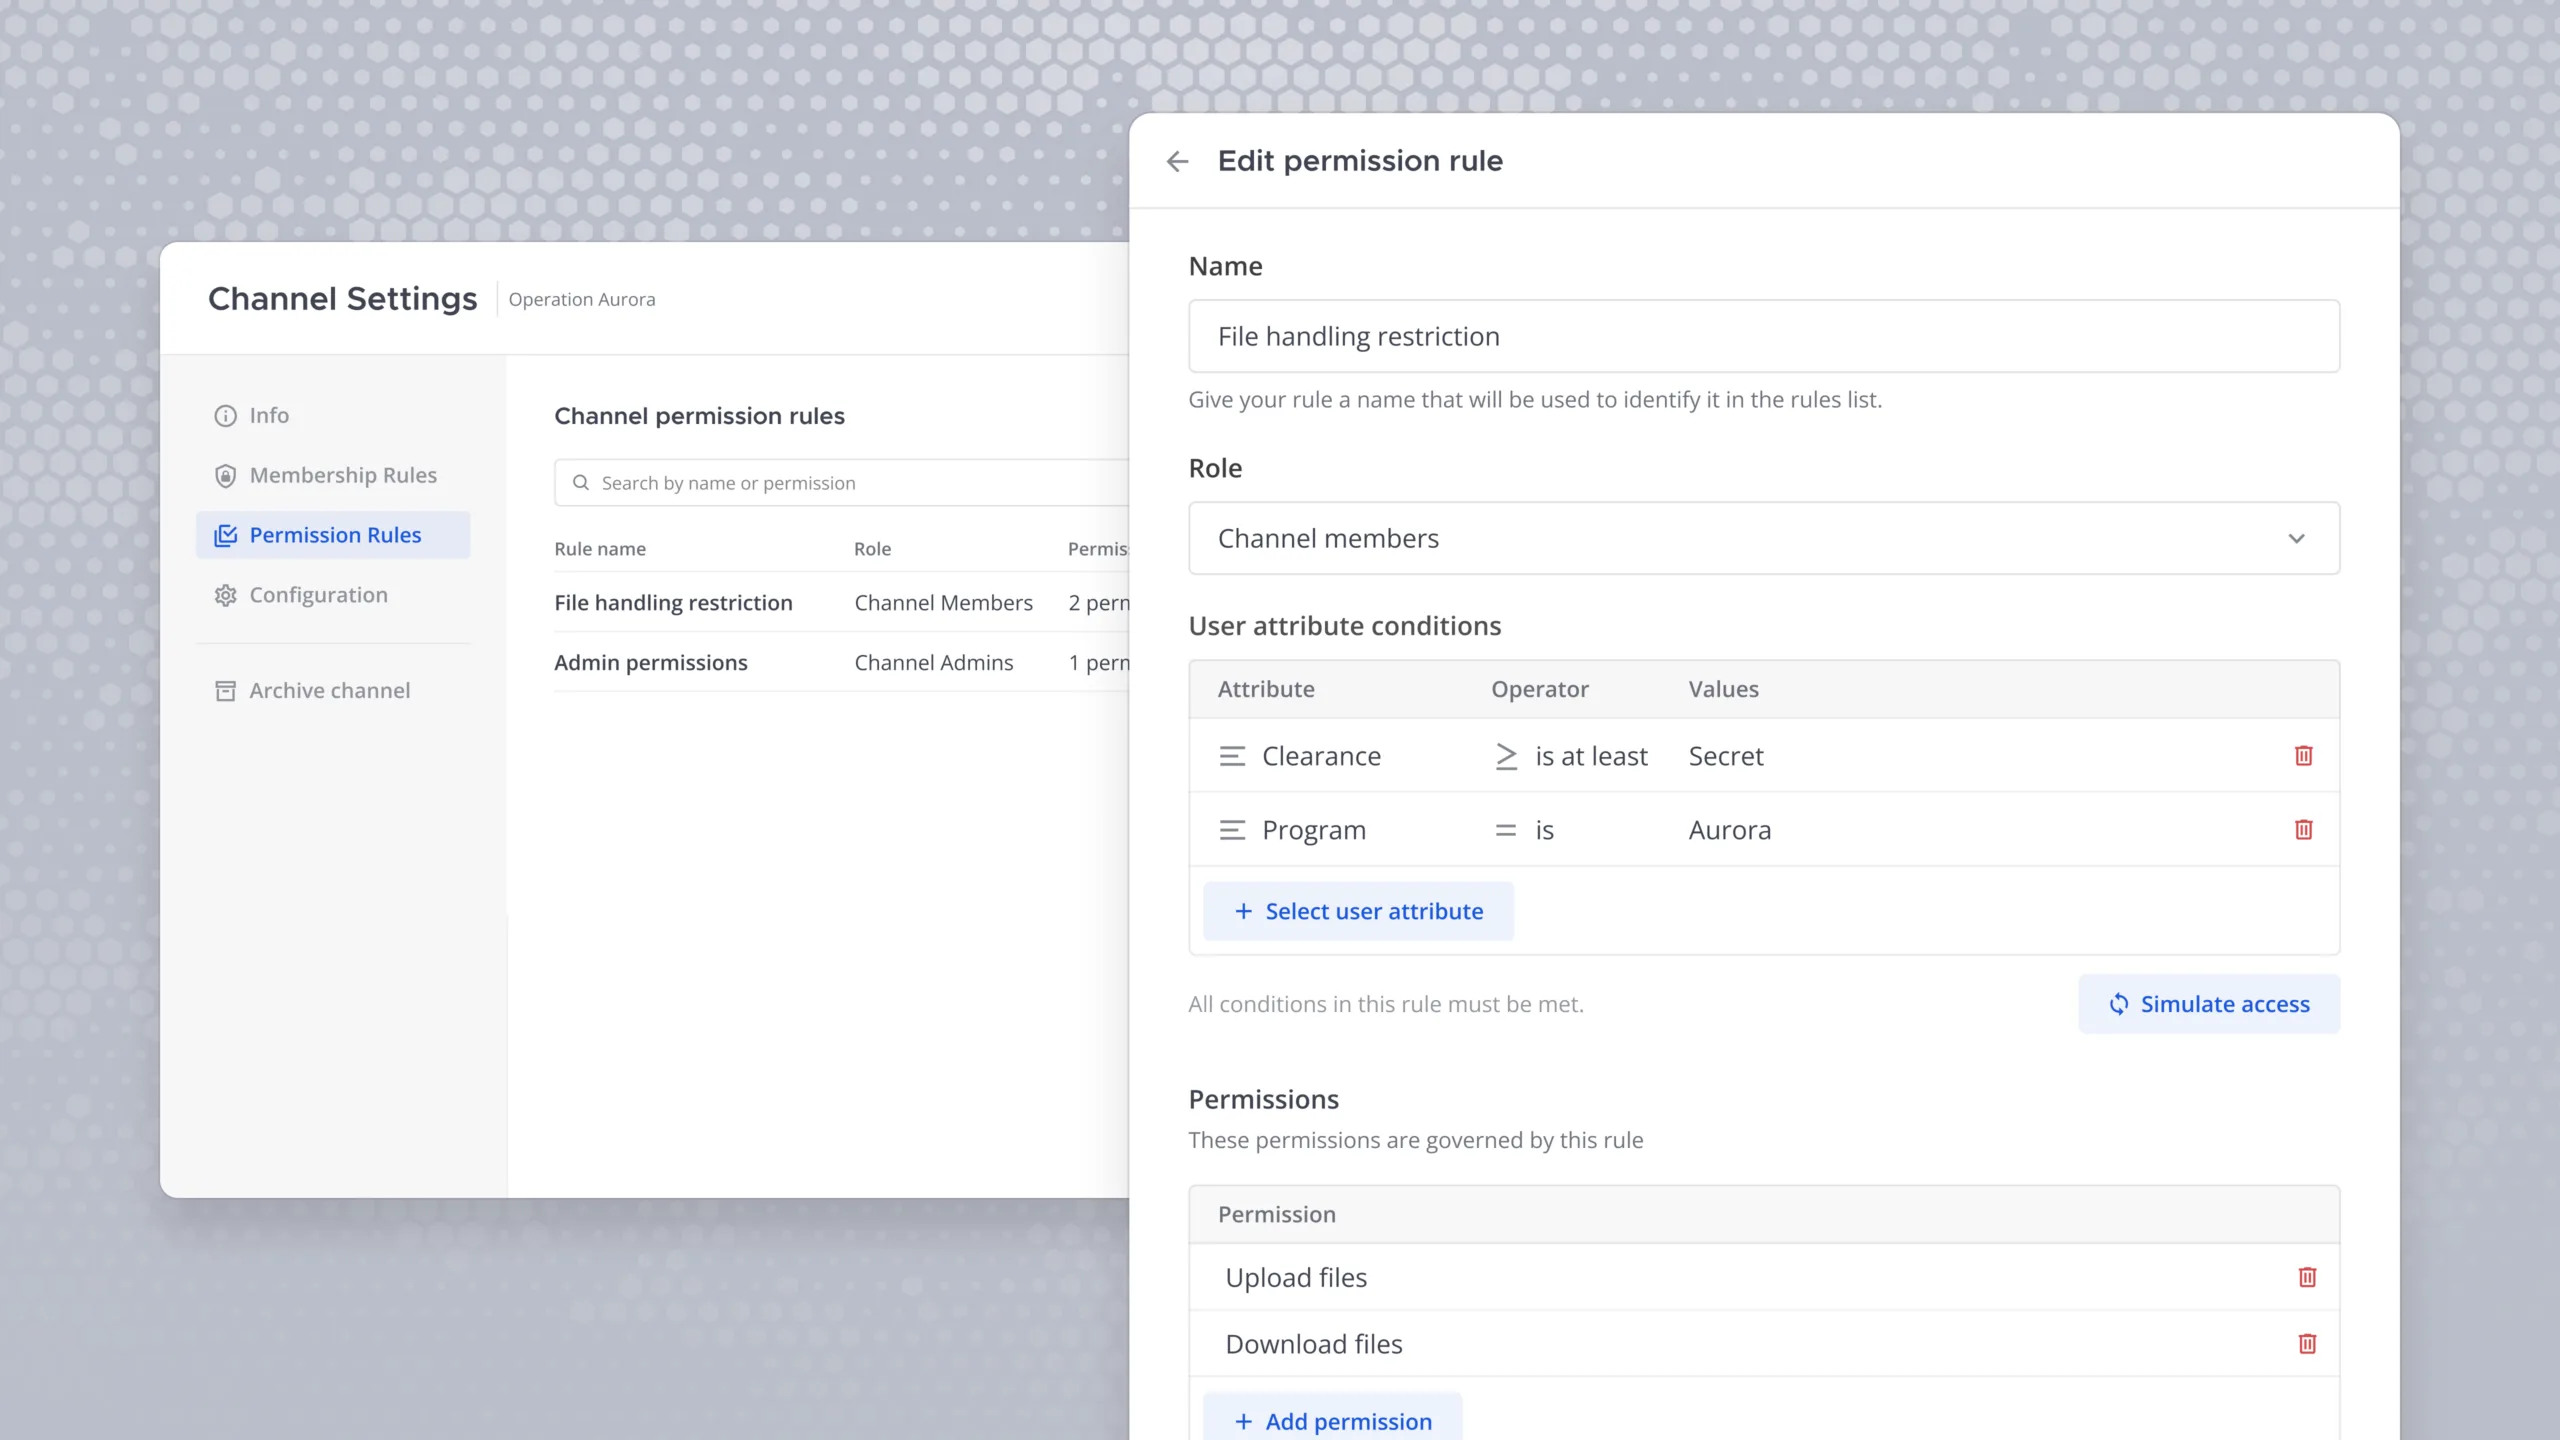
Looking forward, leveraging Mattermost’s attribute-based access controls (ABAC) will only make Cross Guard more powerful. Instead of waiting until information is accidentally shared with separate agencies or allied partners, combining ABAC with cross domain sharing passes attributes across the boundary to allow policies to be built and managed independently on each side allowing data to move safely with operators staying focused.
Also in Mattermost v12: access controls and agent workflows
Cross Guard is just one of the three pillars that support Mattermost v12. Also in v12 are advancements in our ABAC policies using Hierarchical Attributes and Environmental Attributes allowing you to evaluate a user’s current state and rank attributes in policy enforcement. This drives the fine-grained controls the agents inherit from their users.
Finally, with Agentic Workflows, Mattermost leverages the previous Agents V2 work to use sovereign AI models entirely within your data boundaries. Once again, you have complete control over your data and where it does or does not travel ensuring your teams have the tools they need in the environments they operate within. (Read more about agent access controls in v12.)
Mattermost v12 is available now. For air-gapped, sovereign, and classified configurations, contact your account team or get started.